Quick answer
On October 29, 2026 at 20:24 UTC, an attacker drained Binance hot wallets across Ethereum, Bitcoin and Tron. Binance puts the total impact at about $6.3B. Its first findings point to a compromised DevOps engineer's laptop, not a leaked private key. On-chain analysts trace the Ethereum leg to a malicious EIP-7702 delegate installed on the "Binance 14" hot wallet. Binance says about $3B is now frozen. About $1.85B in native BTC and ETH can't be frozen. The attacker is splitting altcoins out to new wallets one token at a time and swapping them for ETH.
StalkChain data adds three things. The attacker rehearsed the drain on a dummy wallet four hours earlier. He used Aave to turn $60M of freezable USDT into ETH minutes before Tether acted. And about 470,900 ETH (~$1.04B) now sits in six wallets that haven't sent anything to a mixer, bridge or exchange.
Binance hack in numbers
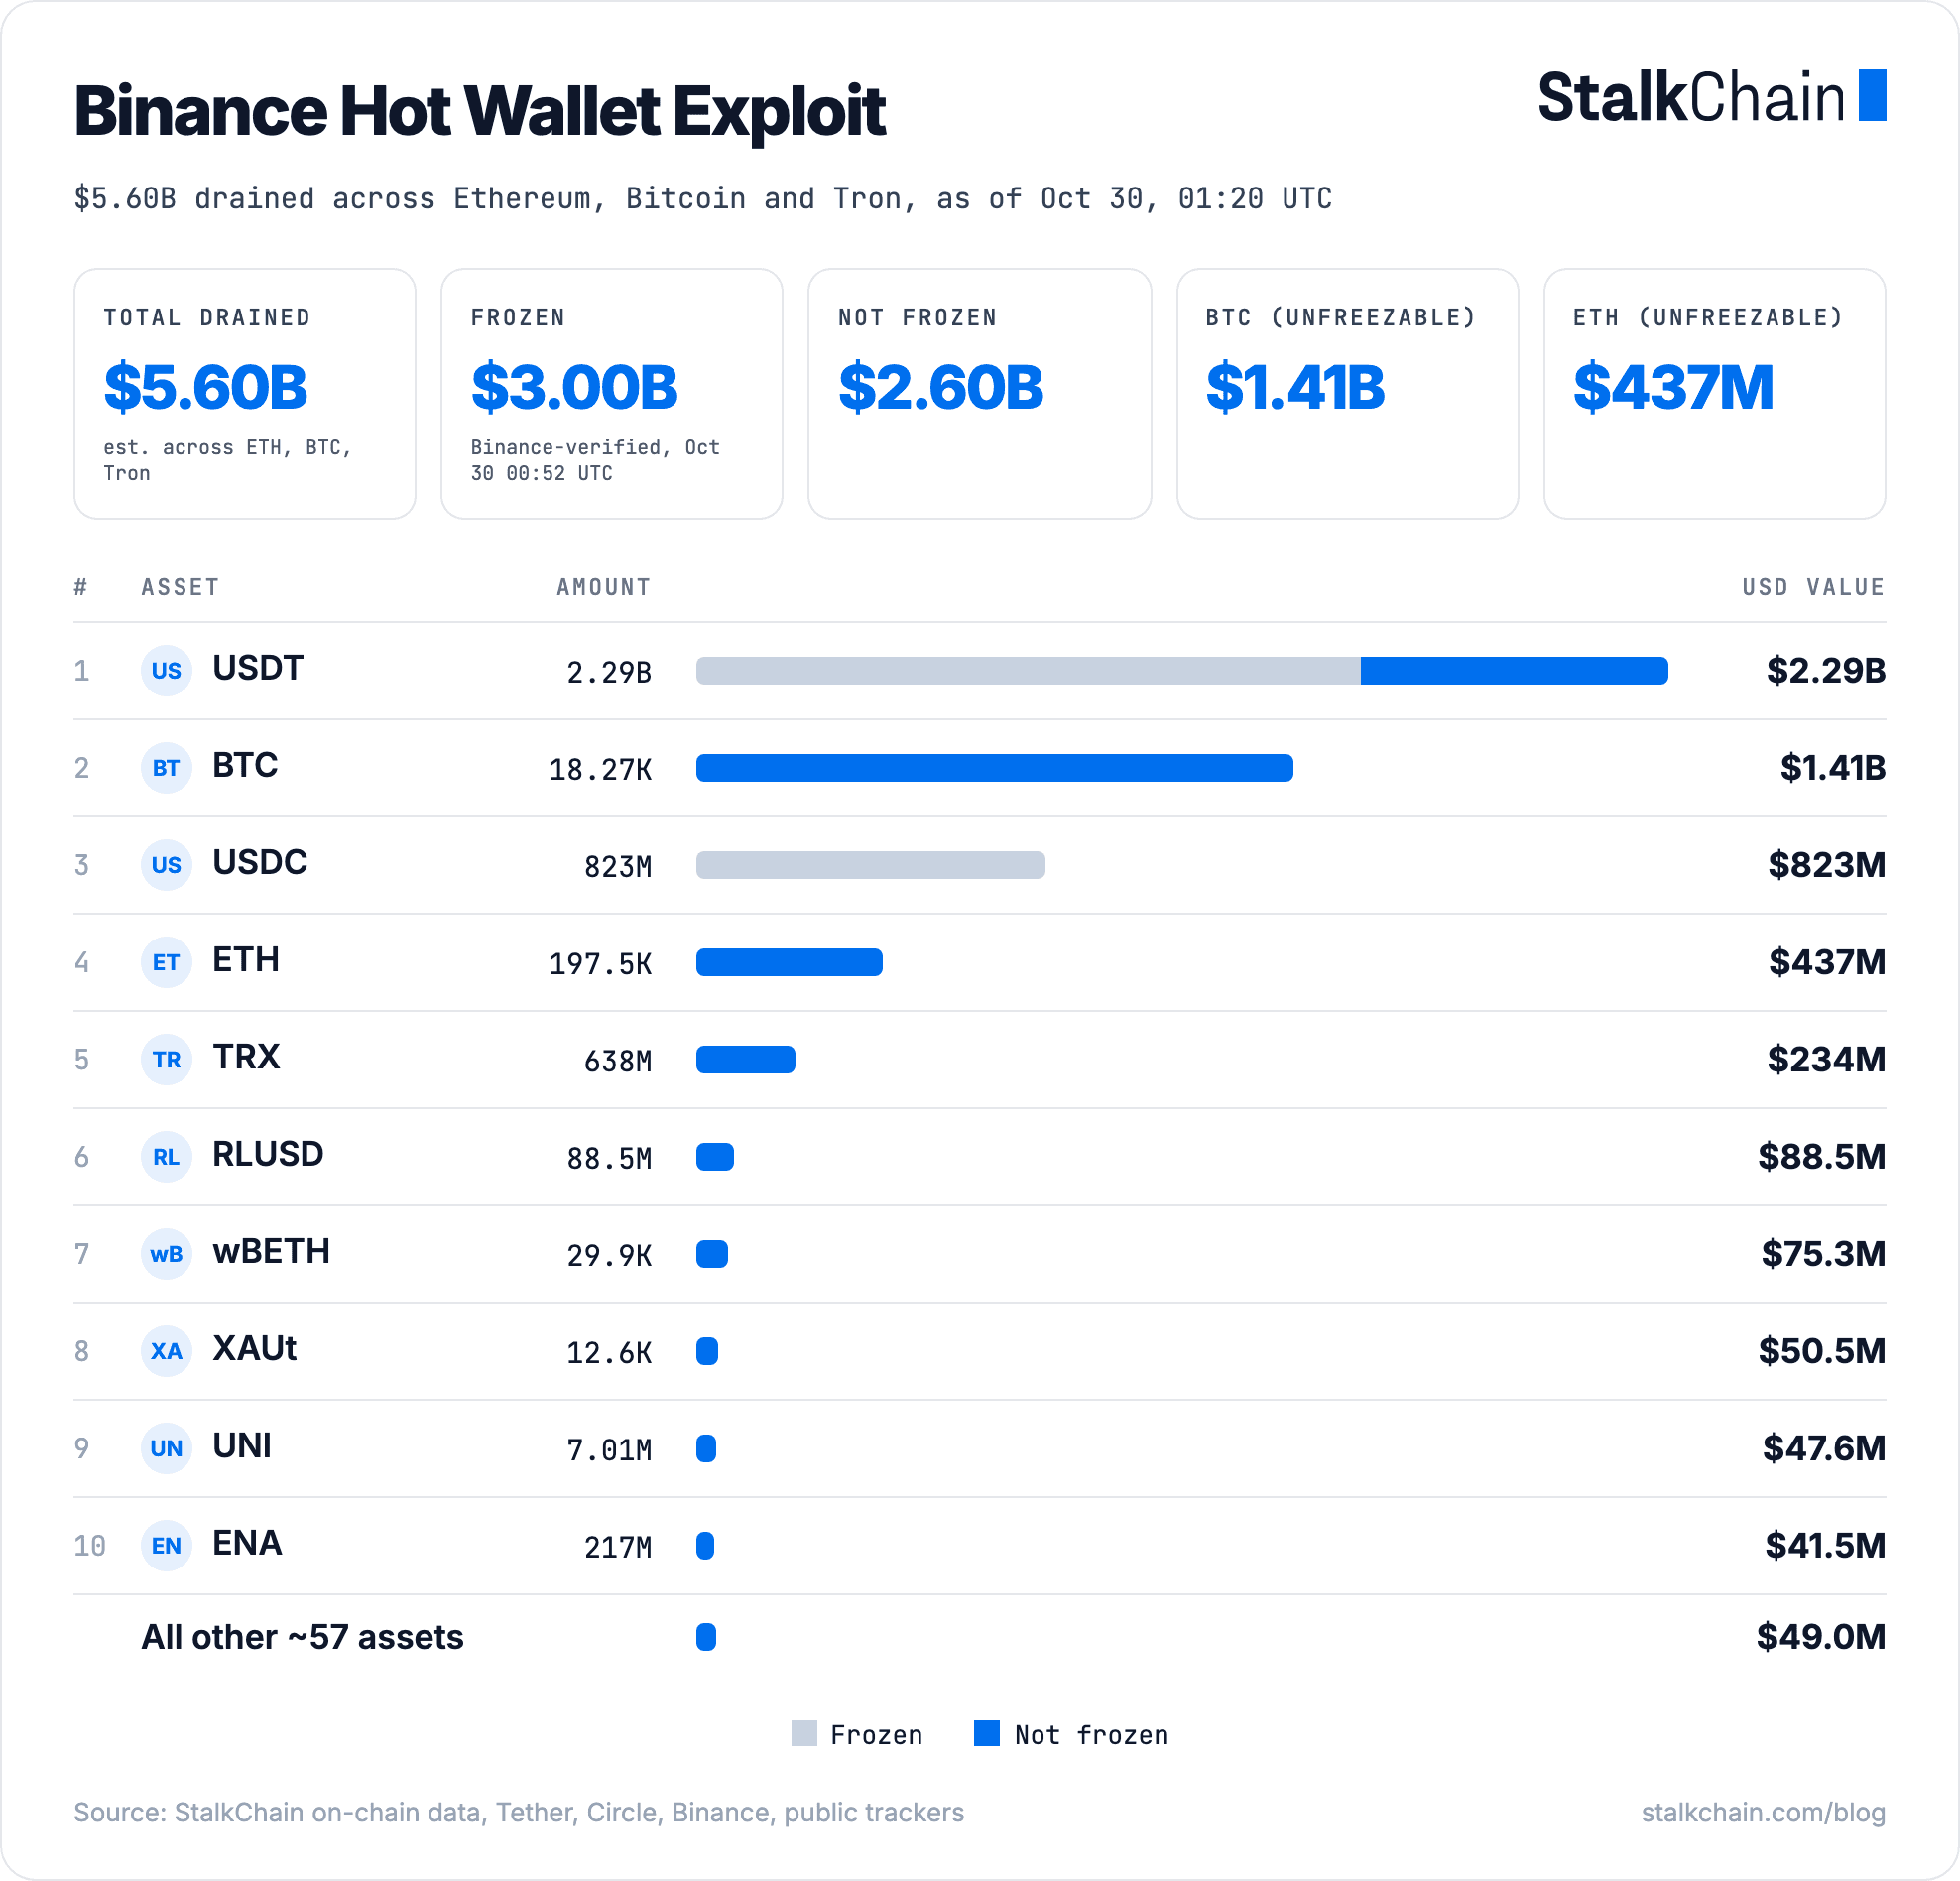
This is the largest crypto theft on record, about 4.2x the $1.5B Bybit hack of February 2025. Binance's own estimate is about $6.3B. On-chain tallies come to about $5.6B, and StalkChain's hack database lists $5.78B across seven chains. We use Binance's figure. The gap may be assets not yet traced on-chain or price moves since the drain.
How the attack worked
Binance's first findings (02:25 UTC, Oct 30): a DevOps engineer's laptop was compromised. That gave the attacker access to a service container, which he used to submit unauthorized withdrawal transactions. Binance says it found no evidence of a wallet private key leak, and has revoked the affected address authorisation. A detailed technical post-mortem will follow.
This is what the chain shows, as reconstructed by independent analysts (0xQuit, StarPlatinum) and checked against StalkChain wallet data where we cover the chain:
- Gas from Tornado Cash. Between Oct 28 and Oct 29, a setup wallet (
0x7C86…5CA0) got three ~0.1 ETH withdrawals from the Tornado Cash 0.1 ETH pool. - Delegate contract deployed (~16:00 UTC). The setup wallet deployed a drain contract (
0x63e8…6fAe) with asweep(address, address[])function. - EIP-7702 authorization (~20:24 UTC). The relayer submitted an EIP-7702 authorization that installed the malicious code on the Binance 14 hot wallet (
0x28c6c06298d514db089934071355e5743bf21d60). - One-transaction sweep. Calling Binance 14 ran the delegate code. It moved ~$2.53B across 63 tokens to a wallet created that day,
0x5227f603c1ee34ce3c06efe6477003bdfccb2f8c. - Second hot wallet, 24 seconds later. Binance 16 sent another 28,005 ETH to the same place. Analysts say the same delegate was used to pull USDC from a third Binance hot wallet. StalkChain data shows the main receiver now holds exactly 823M USDC.
The relayer suggests the attacker held signed EIP-7702 authorizations, not private keys. With the keys, they could have moved everything directly. That points to a signing-flow compromise, and Binance's first findings fit it: no leaked key, but an attacker inside a service that could submit transactions. Binance hasn't yet said how that access produced the EIP-7702 authorization. Earlier the same day, CZ had warned about a front-end injection attack that shows users a valid transaction but gets them to sign a different one. No one has publicly linked the two incidents.
He rehearsed the attack first
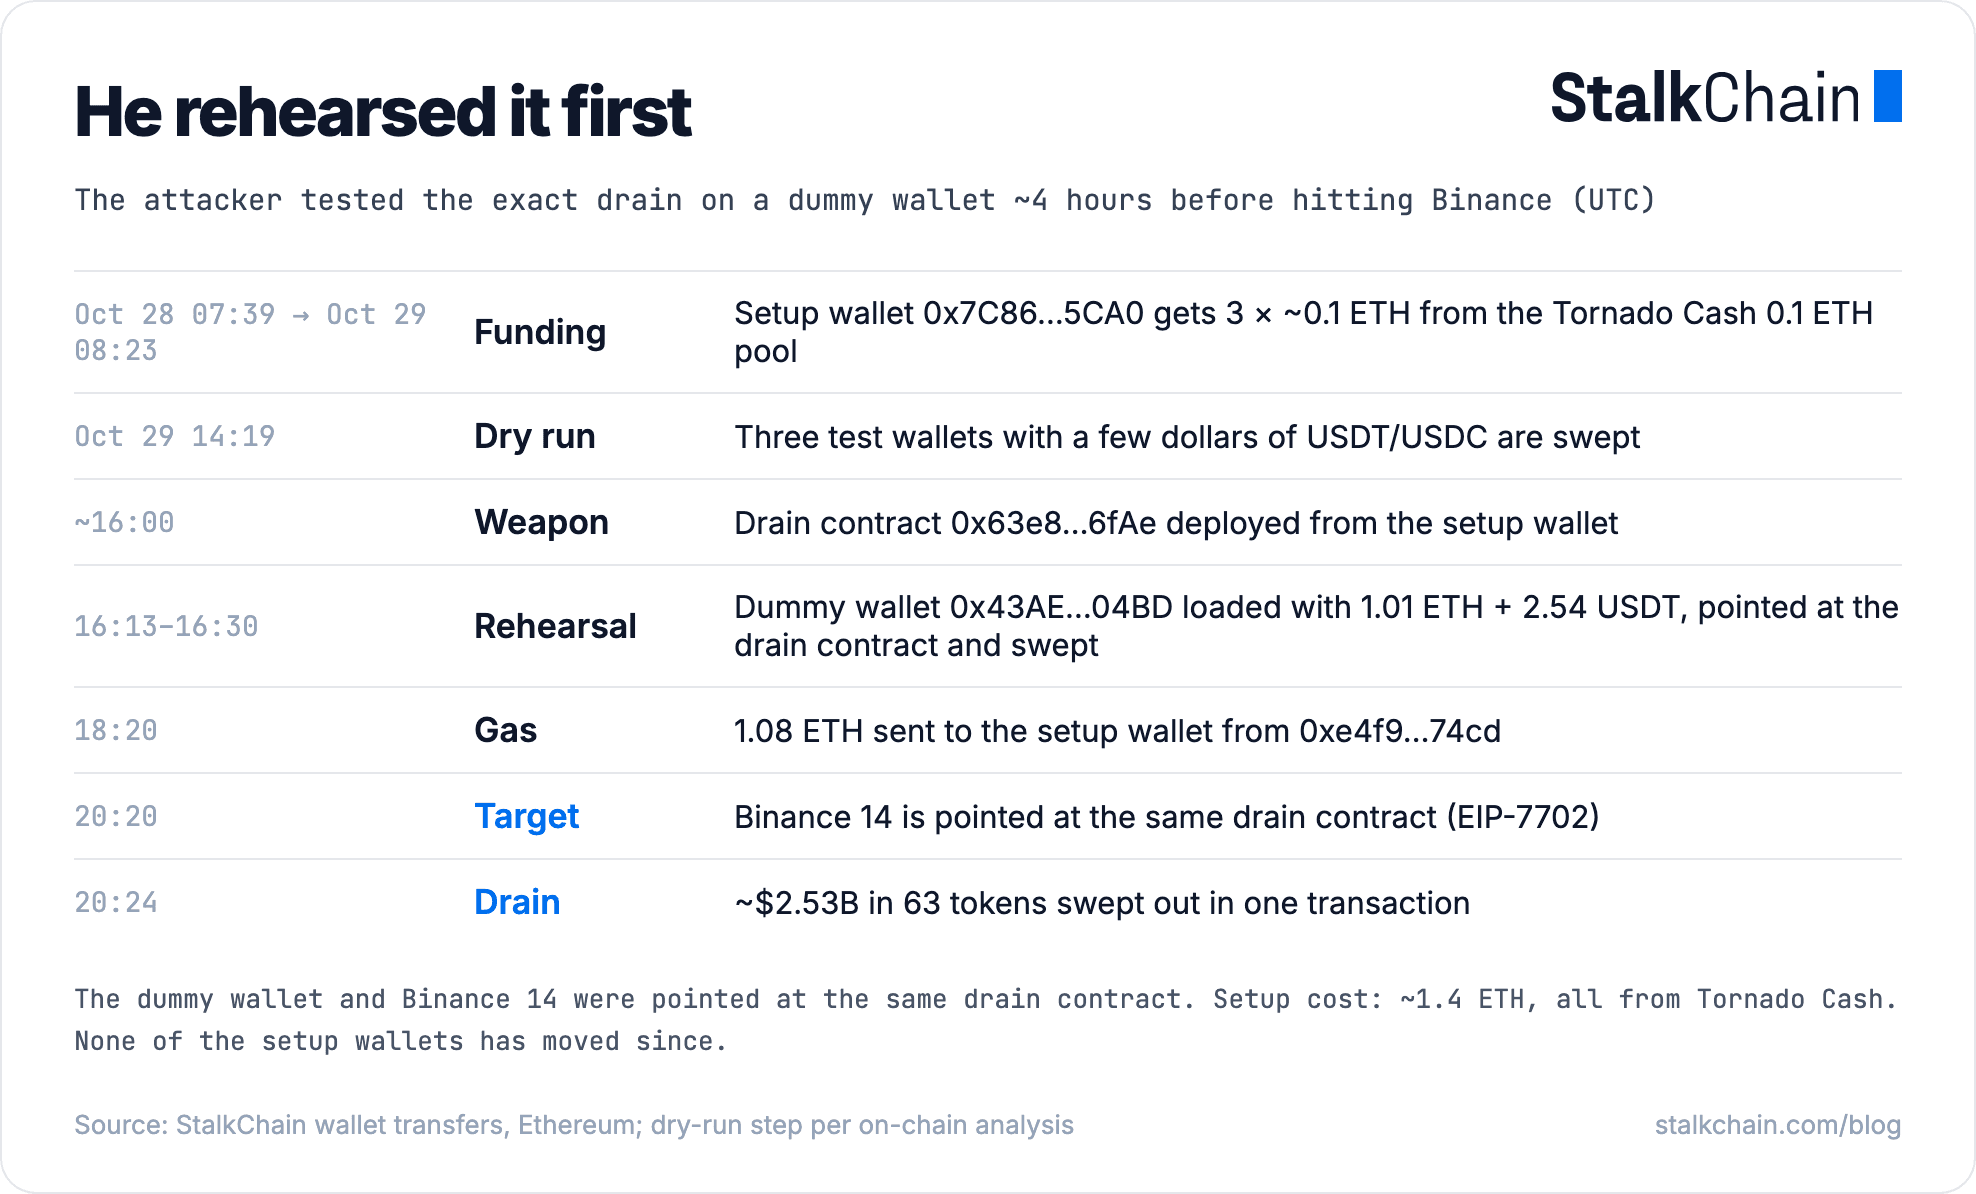
The drain wasn't improvised. StalkChain transfer data shows the attacker tested it end to end on a wallet he controlled about four hours before hitting Binance.
- Funding. The setup wallet
0x7C8601d4645b93cea45F71e118A729332e6B5CA0got exactly three ~0.098 ETH payments from the Tornado Cash 0.1 ETH pool: Oct 28 at 07:39 and 08:53, and Oct 29 at 08:23. Two more wallets used in the tests were funded the same day, which on-chain analysts also trace to Tornado Cash. - Dry run (14:19). Three test wallets holding a few dollars of USDT and USDC were swept, per on-chain analysis of the setup wallets.
- Rehearsal (16:13–16:30). Dummy wallet
0x43AEdb9BAD6219677a2C8D6858321C16988404BDgot 2.54 USDT and 1.01 ETH. It was then pointed at the same drain contract through EIP-7702 and swept. The USDT left at 16:30. - Gas top-up (18:20).
0xe4f9…74cd, the wallet that funded the dummy, sent 1.08 ETH to the setup wallet. - The real thing (20:20–20:24). Binance 14 was pointed at the same contract and drained.
The whole setup cost about 1.4 ETH. None of the setup wallets has moved since. If one of them ever touches an exchange, it could identify the attacker, so we're watching all of them.
How he beat the freeze: the Aave move
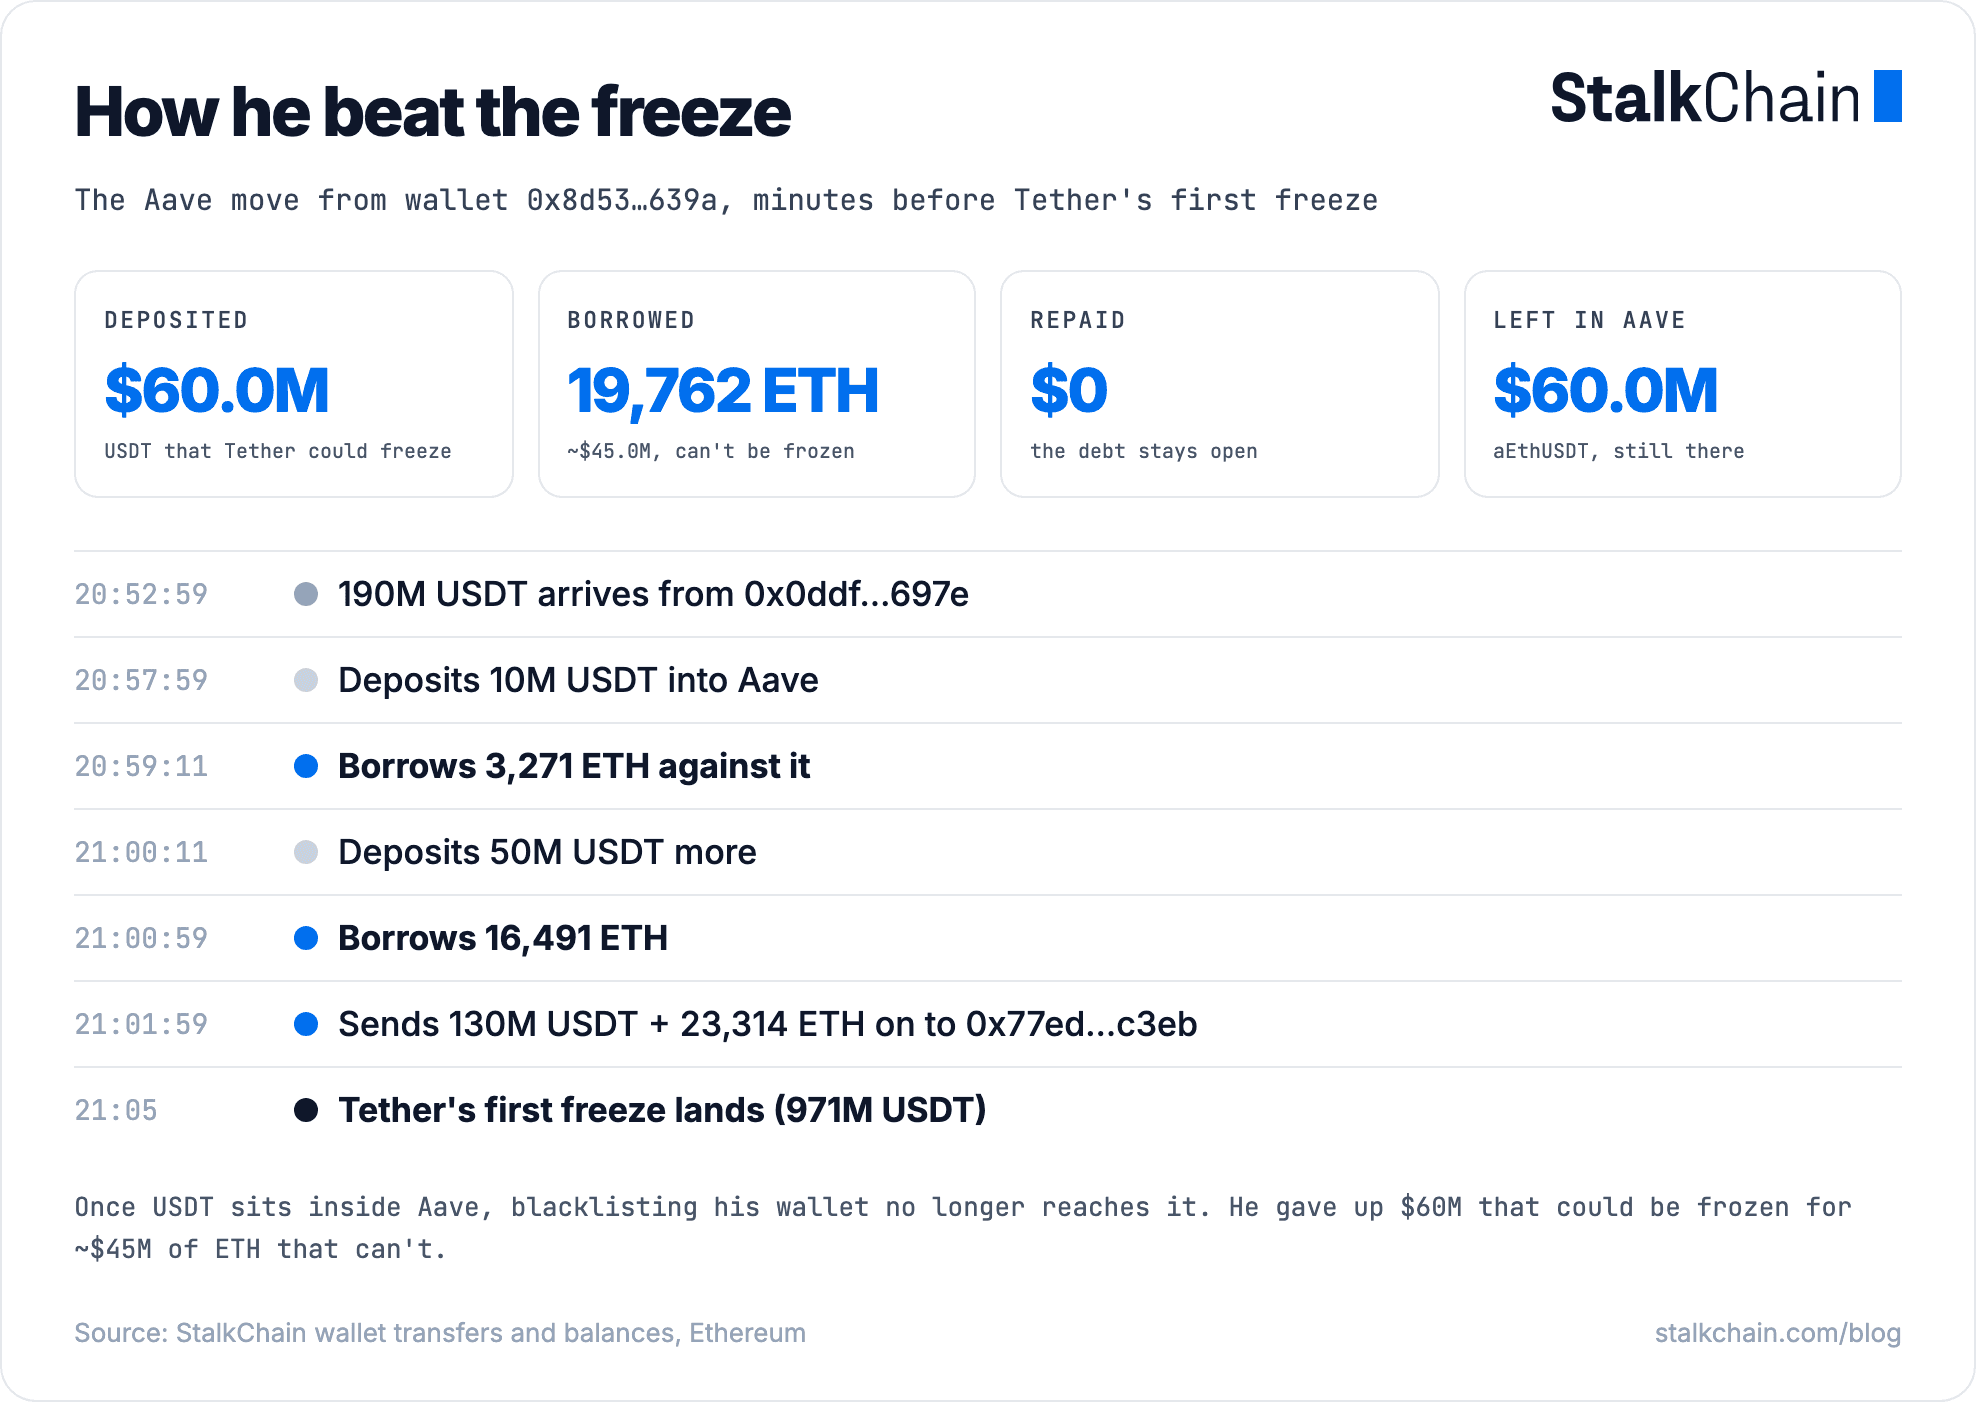
Tether and Circle can freeze stablecoins by blacklisting the wallet that holds them. Nobody can freeze ETH. So the attacker's first job was to turn as much USDT into ETH as possible before the freezes landed.
About 700M USDT left the main wallet within nine minutes of the sweep, before Tether acted. Most of it was swapped straight to ETH on DEXs. One 190M USDT slice went to wallet 0x8d53903625b8e839b9df4bd28b0efb1cd6b8639a, and StalkChain data shows what happened next, to the second:
| UTC | What happened |
|---|---|
| 20:52:59 | 190M USDT arrives from 0x0ddf…697e |
| 20:57:59 | Deposits 10M USDT into Aave |
| 20:59:11 | Borrows 3,271 ETH against it |
| 21:00:11 | Deposits another 50M USDT |
| 21:00:59 | Borrows 16,491 ETH |
| 21:01:59–21:02:35 | Sends the remaining 130M USDT and 23,314 ETH on to 0x77ed…c3eb |
| 21:05 | Tether's first freeze lands (971M USDT) |
Why it worked:
- The freeze can't reach it. Once deposited, the USDT sits in Aave's contract, not in his wallet. Blacklisting his address no longer touches it.
- The loan is the cash-out. He never intends to repay. He gave up $60M of USDT that could be frozen and kept ~$45M of ETH that can't. That's about 75% of the value instead of nothing.
- No counterparty. Two borrows, no order book, nobody to approve them.
The $60M of collateral (aEthUSDT) is still in that wallet, and the 19,762 ETH debt is unpaid. Aave says its contracts weren't exploited and has since frozen the affected markets. Aave was a cash-out route here, not the target.
Where the stolen funds are right now
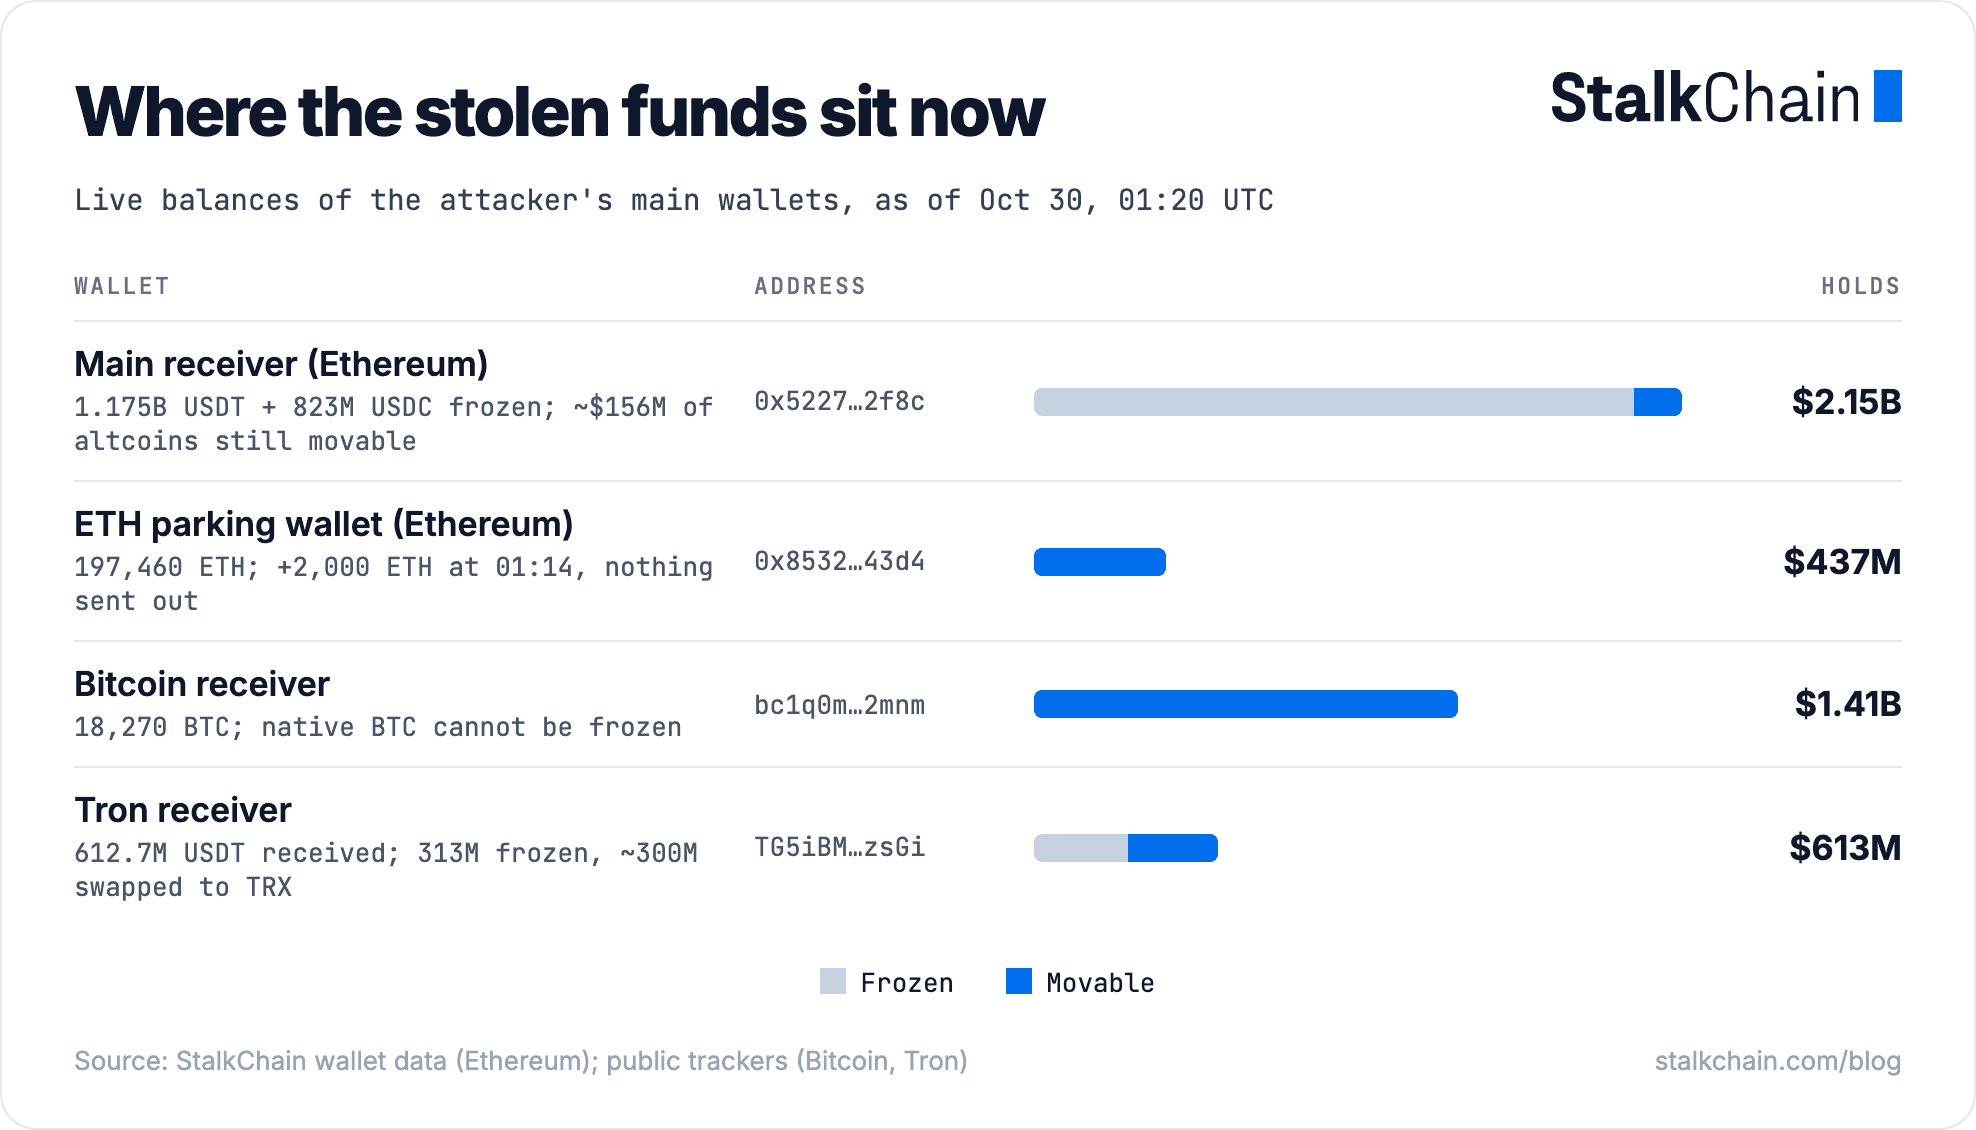
StalkChain wallet data for the two main Ethereum addresses, as of 01:20 UTC:
| Wallet | Holds | What's in it |
|---|---|---|
0x5227…2f8c main receiver | $2.15B | 1.175B USDT and 823M USDC, both frozen. About $156M of altcoins (XAUt, USD1, PAXG, FDUSD and 40+ others) can still be moved. |
0x8532…43d4 ETH parking wallet | $437M | 197,460 ETH. It got 2,000 more ETH from the main receiver at 01:14 UTC. Nothing has left it. |
On Bitcoin and Tron we rely on public trackers: 18,270 BTC at bc1q0mtc2f5agpkvlq6hhahmfr3hlr55kyfjhl2mnm, and 612.7M USDT at Tron address TG5iBMQPrDzJJAUM8GMVBf1hRaJ1wvzsGi (313M frozen, about 300M swapped to TRX).
The altcoin peel-off
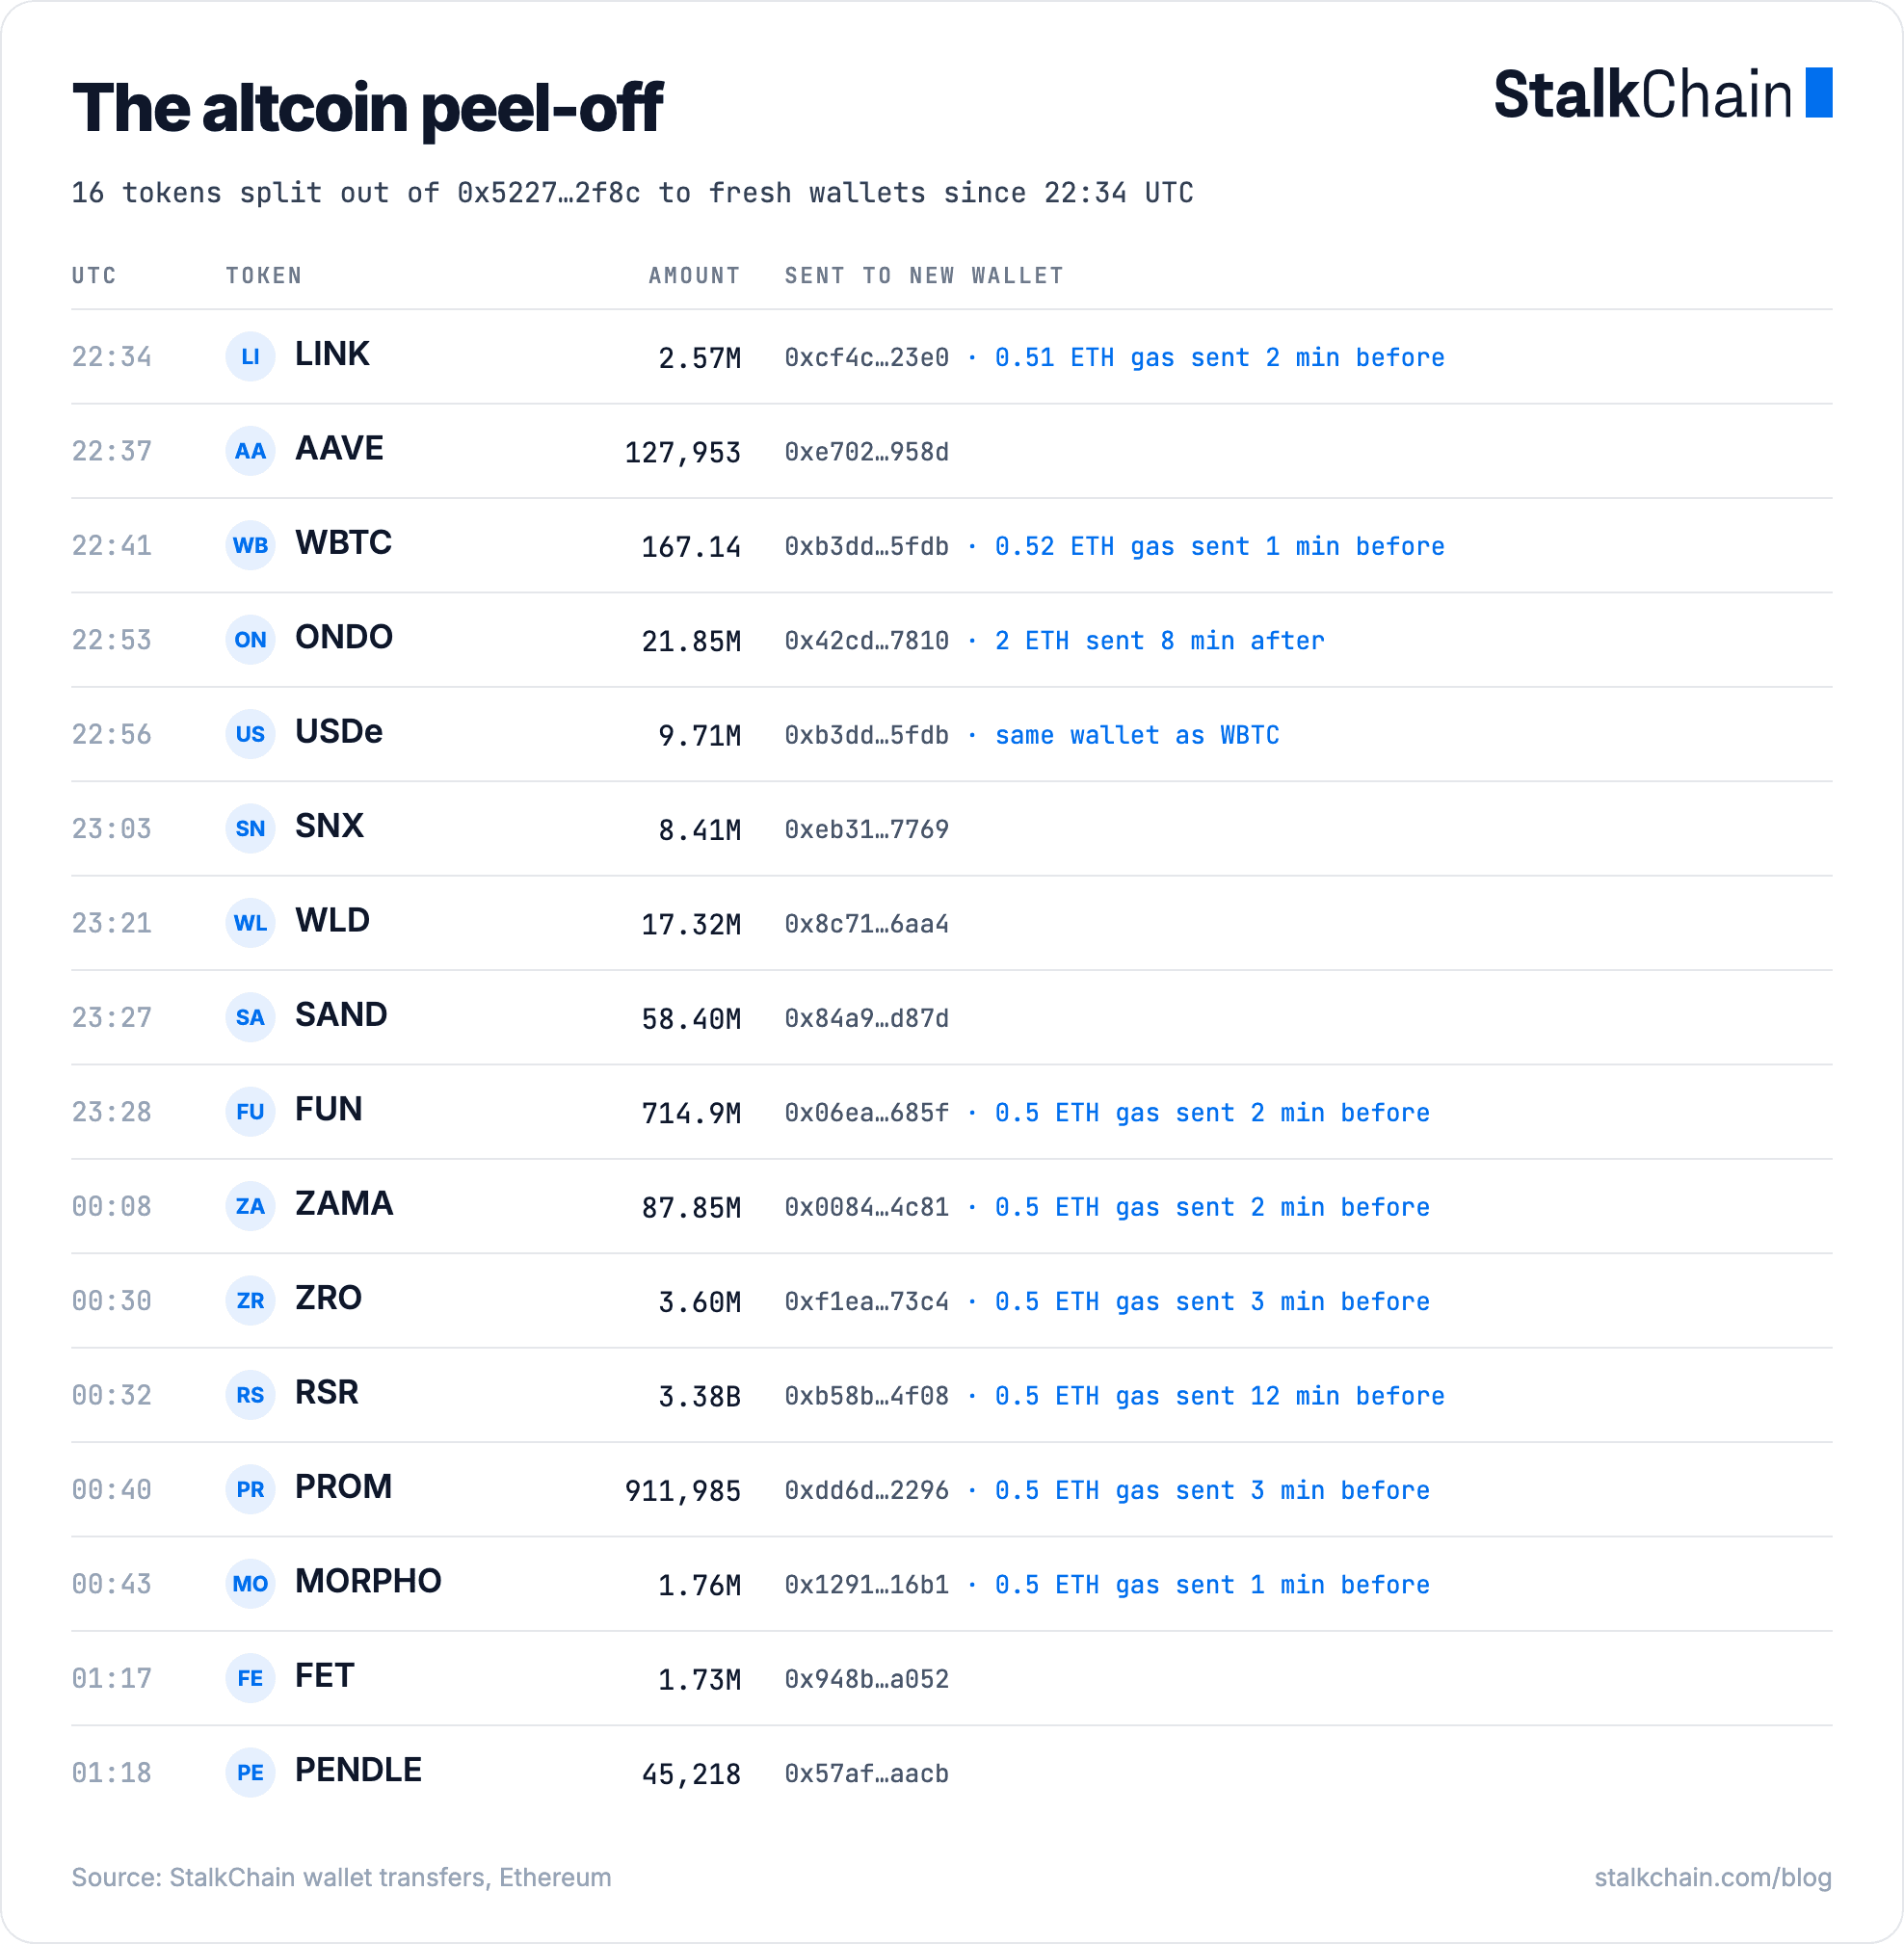
From 22:34 UTC, StalkChain transfer data shows a steady pattern. Every few minutes, the main wallet sends one altcoin to a brand-new address. Most of those new wallets get ~0.5 ETH for gas a minute or two first. By 01:18 UTC, 16 tokens had moved this way, including 2.57M LINK, 127,953 AAVE, 167 WBTC, 21.85M ONDO and 3.38B RSR. The two latest, 1.73M FET and 45,218 PENDLE, went out without a gas top-up first.
Not every move goes one way. At 01:16 UTC the ZAMA wallet sent 53.33M ZAMA back to the main receiver, about 61% of the 87.85M it got at 00:08. Lookonchain reports that the attacker has sold its UNI, ENA, PEPE, LINK, AAVE, ONDO and WLD for 70,480 ETH (~$158M).
Splitting into single-asset wallets makes each pile smaller and harder to watch. It also lets the attacker sell through DEXs before more issuers or exchanges block the tokens. The main wallet is also getting a stream of dust transfers (6.9e-17 ETH) from 0xcb02…4435. That looks like address-poisoning spam, a common sight on any wallet in the news.
How the money is being laundered so far
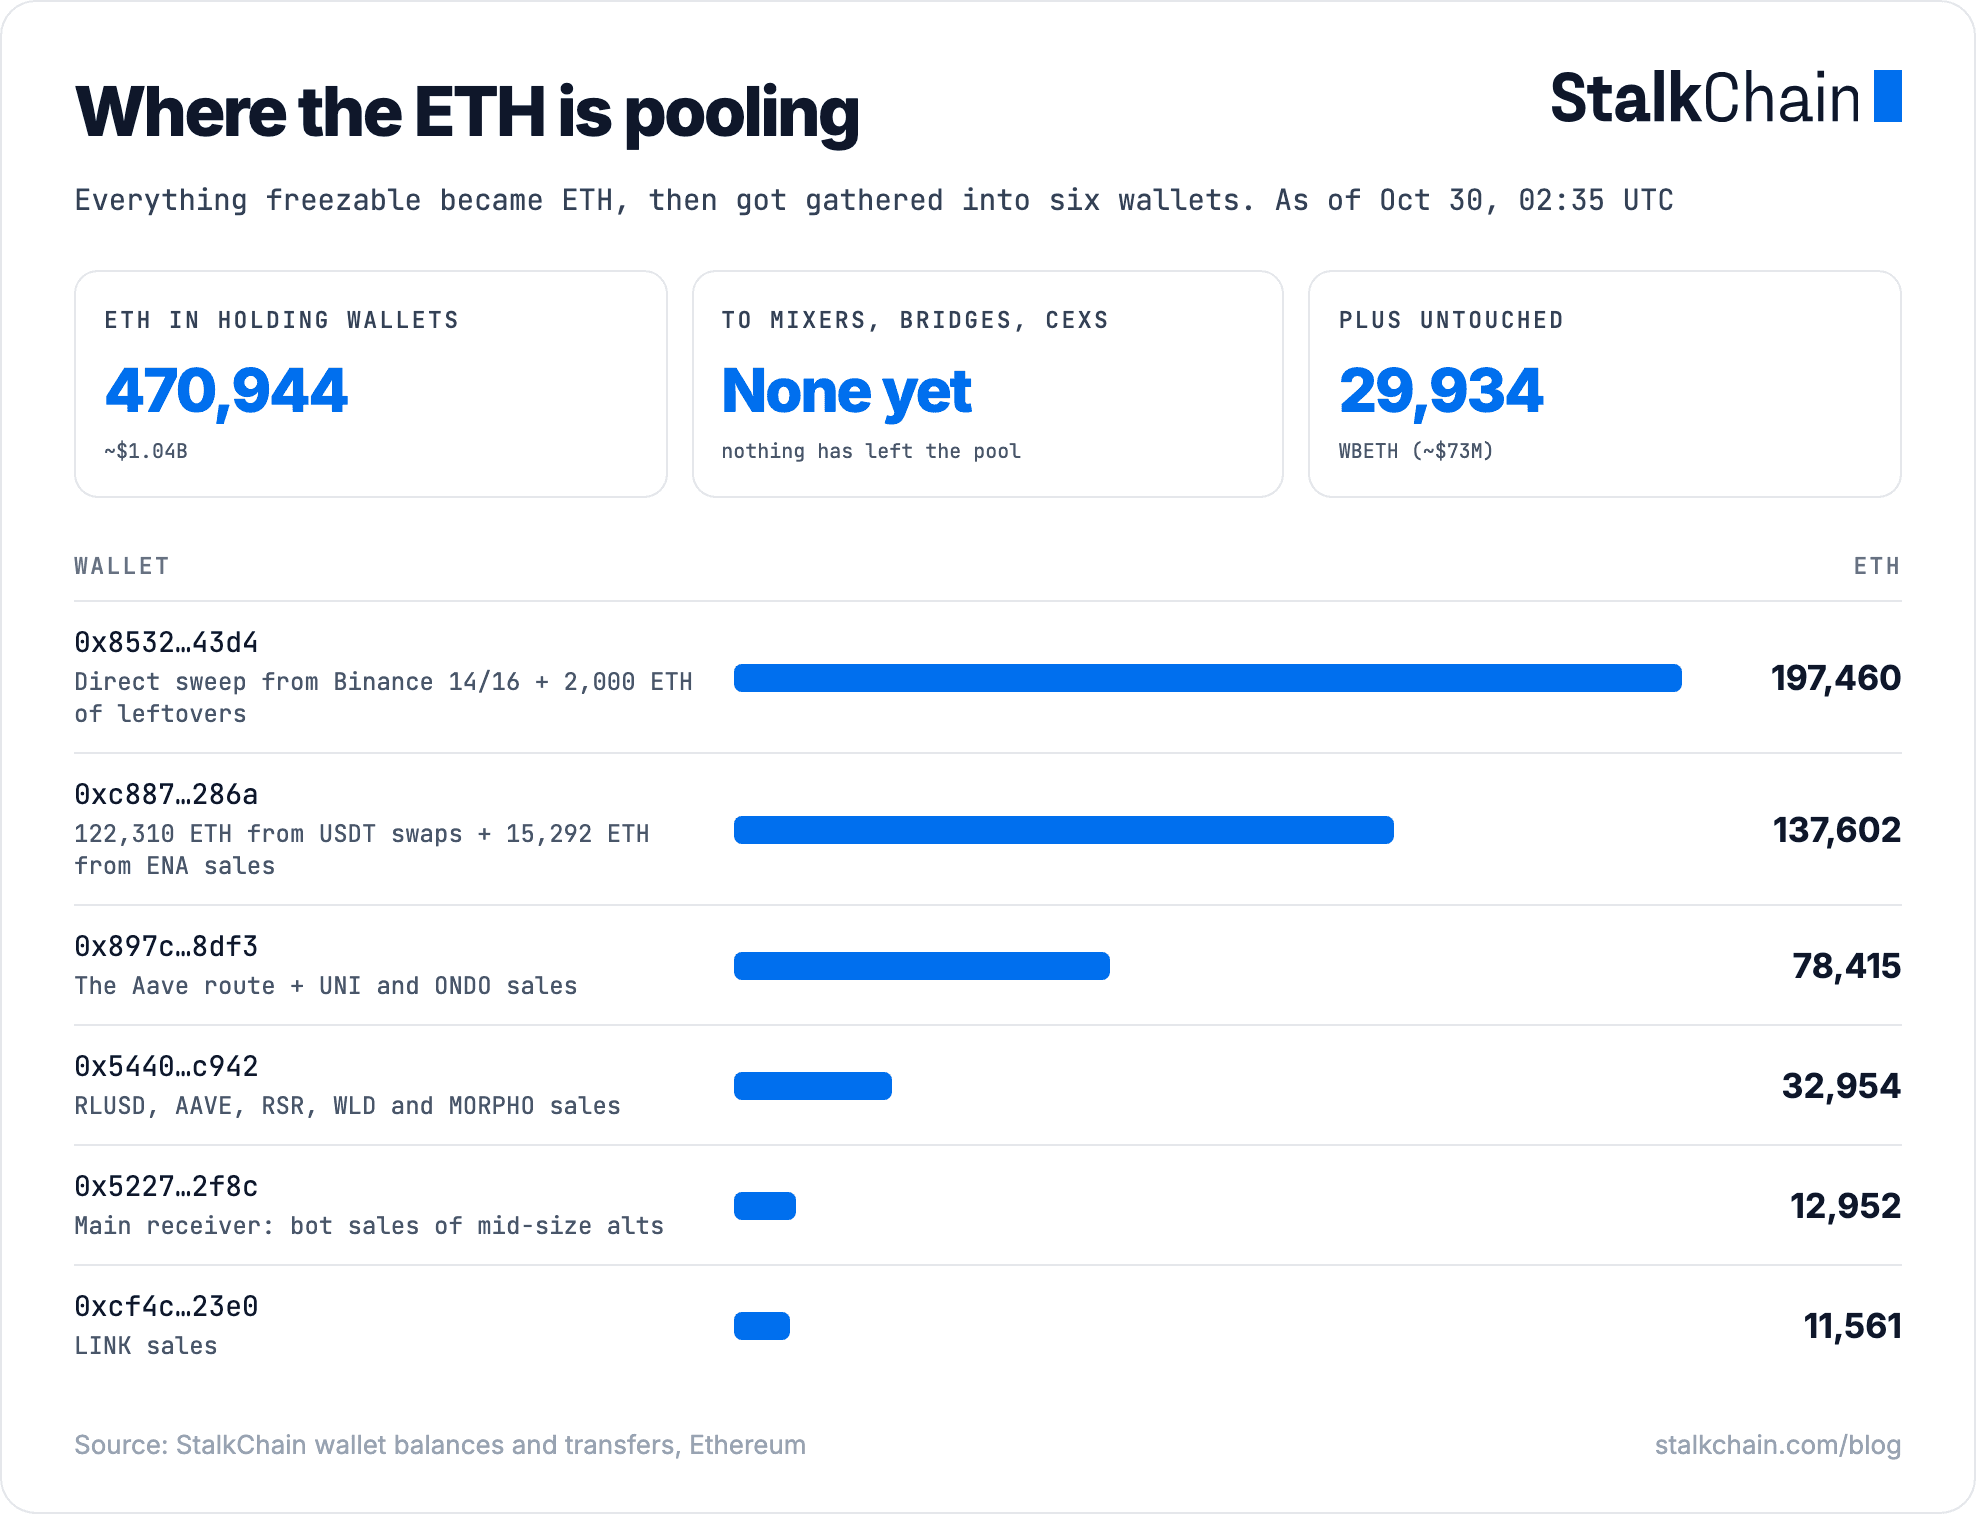
So far the attacker isn't really hiding the money. He's converting it and gathering it into a few wallets. We checked every wallet we've mapped: nothing has gone to a mixer, a bridge, a cross-chain swap or an exchange yet. What he has done falls into three stages.
- Swap anything freezable into ETH. The USDT that escaped the freeze, the Aave borrow, RLUSD, and one altcoin after another. One swap wallet,
0x9749…c762, collected about 122,300 ETH from DEX fills between 20:34 and 20:49 UTC. - Hop through layers of wallets. The Aave branch passed through seven wallets in about 75 minutes. Each hop swaps part of the money and forwards the rest. It's basic hopping to make the trail harder to follow, not real mixing.
- Gather the ETH. About 470,900 ETH (~$1.04B) now sits in six wallets. Roughly 195,500 ETH of that was swept as ETH. The other
275,000 ETH ($610M) came from swaps, sales and the Aave loan.
Since about 01:30 UTC the main wallet has stopped using a fresh wallet per token. It now sells mid-size altcoins itself, in small slices every 12–60 seconds, straight into DEX pools. 1INCH, QNT, GTC, EIGEN, LDO, ETHFI, COMP and CFG went this way. The ETH from those sales stays in the main wallet.
Bitcoin. The Bitcoin leg moved first, at about 20:20 UTC, minutes before the Ethereum sweep. Public explorer data (mempool.space) shows the 18,270 BTC split into exact 1,000 BTC lots in quick succession. About 17,270 BTC (~$1.33B) sits in 18 addresses and hasn't moved since.
Tron. The 612.7M USDT arrived at 20:22 UTC. 300M was swapped for TRX on SUN.io before the freeze. The 638.2M TRX (~$220M) sits in TSpe5HC3PRD2svJcr1YoGszhHk2mtkyZ8A, untouched. The remaining 312.7M USDT matches Tether's frozen figure.
What usually comes next. After the February 2025 Bybit hack, Lazarus converted most of the stolen ETH to BTC through THORChain within days. The signs to watch here are a holding wallet splitting into many small ones, or ETH reaching THORChain, Chainflip or eXch.
Who did it? North Korea, and two false leads
No government agency or analytics firm has attributed the hack. Circle says its freeze was done in coordination with law enforcement.
What fits North Korea's past hacks. The attacker abused the signing process instead of stealing a key outright, like the Bybit hack (attributed to North Korea by the FBI) and the Bitget hack in September. The setup was funded through Tornado Cash, with a dry run and a full rehearsal. Anything freezable was swapped to ETH within minutes. Two days earlier, Binance said it had blocked North Korea-linked fake job interview attacks.
What doesn't fit, yet. EIP-7702 hasn't been used at this scale in an attributed North Korean hack. There's no ETH-to-BTC laundering through THORChain so far, which started within days after Bybit. And we found no transfer to or from any known Lazarus address. We don't have the analytics firms' private address labels, so we can't rule a link out.
False lead 1: the "Kelp DAO hacker" link. A widely shared claim said the attacker is the same group that hit Kelp DAO in April, because 74.56M ARB went to an address Arkham labels "Kelp DAO Hacker". On Arbitrum, that address is the vault where the Arbitrum Security Council parks frozen funds. It froze Kelp's funds there in April and this attacker's 74.56M ARB and 8,425 ETH (~$30.5M) there today. The two hacks share a freezer, not a hacker.
False lead 2: the hacker's short. Lookonchain posted a Hyperliquid wallet, 0x8added25f8cce417c1e19aad91fb6ddcb9917d2c, that shorted ETH and BTC around the hack. We found no transfers between it and any of the 30+ attacker wallets. It's 271 days old with a long trading history, it funded the shorts from its own Aave and Pendle positions, and its ETH short opened at 21:42 UTC, after the hack was public. Its only Binance link is normal withdrawals from Binance hot wallets, which every Binance customer has. Lookonchain itself calls it a trader, not the hacker.
Market reaction
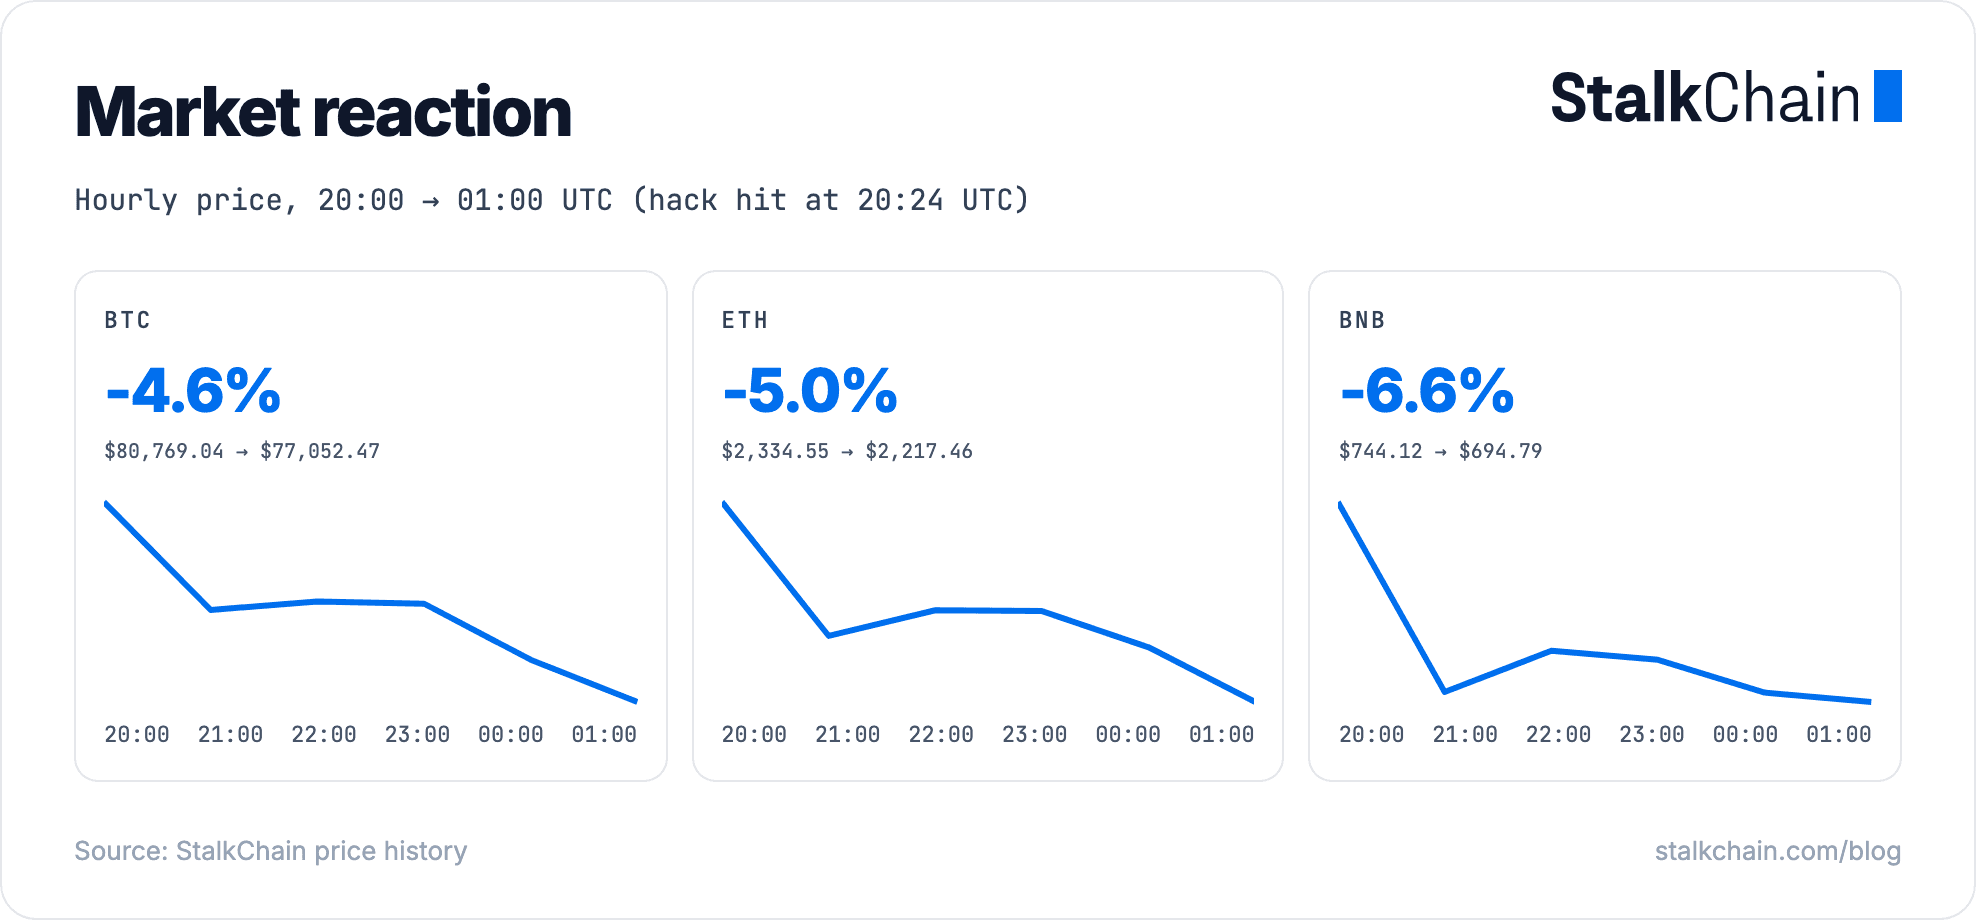
From the 20:00 UTC hourly close to 01:00 UTC, StalkChain price data shows BTC down 4.6% ($80,769 to $77,052), ETH down 5.0% ($2,335 to $2,217) and BNB down 6.6% ($744 to $695). Traders on X reported around $600M of long liquidations in the first hour, as BTC dropped below $78,500.
Hour-by-hour timeline (UTC)
Before the hack
- Oct 28 07:39 → Oct 29 08:23: The setup wallet gets three ~0.1 ETH withdrawals from Tornado Cash.
- Oct 29, 14:19: Dry run: three test wallets with a few dollars of stablecoins are swept.
- ~16:00: The drain contract is deployed from the setup wallet.
- 16:13–16:30: Full rehearsal on dummy wallet
0x43AE…04BD, pointed at the same drain contract. - 18:20: 1.08 ETH of gas money reaches the setup wallet.
- 18:56: CZ flags a front-end injection attack that tricks users into signing the wrong transaction. Separate incident, no confirmed link.
20:00–21:00: the drain
- 20:24:23: Binance 14 sweeps ~$2.53B in 63 tokens to
0x5227…2f8cin one transaction. - 20:24:47: Binance 16 adds 28,005 ETH to the same address. Total ~$2.70B on Ethereum.
- 20:20–20:22: The Bitcoin leg (18,270 BTC) and Tron leg (612.7M USDT) move first, per public explorers.
- 20:30–20:49: About 700M USDT leaves the main wallet before any freeze. One wallet swaps its share for about 122,300 ETH on DEXs.
- 20:32: @spreekaway is among the first to flag it publicly: "Entire Binance wallet drained into new EOA. Contract call was funded by Tornado Cash."
- 20:42: Newswires report $2.77B leaving Binance wallets, "hack unconfirmed."
- 20:57–21:01: The Aave move: 60M USDT deposited, 19,762 ETH borrowed, never repaid.
21:00–22:00: freezes and confirmation
- ~21:00: BTC falls about $2,500 in 45 minutes, to below $78,500.
- 21:05: Tether freezes $971M USDT linked to the attacker.
- 21:13: Circle freezes $823M USDC.
- 21:15: CZ posts: "User funds are safe! It does look like a hack on Binance." He says he expects all user funds to be covered.
- 21:25: Tether CEO Paolo Ardoino says more than 1.567B USDT is frozen.
- 21:29: Binance statement: aware of reports, investigating, user funds safe.
- 21:42: Watcher.Guru posts the $5.6B breakdown. It becomes the most-liked post on the hack.
- 21:48: StalkChain tracks $2.3B sitting in one receiving wallet, including $823M USDC that matches Circle's freeze.
22:00–23:00: the size becomes clear
- 22:01: On-chain tally: $5.60B across Ethereum, Bitcoin and Tron, with $2.38B frozen (source).
- 22:23: CZ: "Loss might be a bit higher than that, but will cover."
- 22:33: Binance pauses withdrawals until the issue is resolved.
- 22:34: The altcoin peel-off begins (LINK, then AAVE, WBTC, ONDO and others).
23:00–00:00: Binance's numbers
- 23:06: Binance pauses Binance Alpha trading.
- 23:07: The main wallet is selling LINK for ETH. LINK is down 9.3% on the day.
- 23:22: Binance says the verified frozen total is $2.54B, and may rise.
00:00–01:00, Oct 30: coverage pledge
- 00:04: Binance co-founder Yi He: "Binance will cover all hacking losses." Deposits and withdrawals are suspended.
- 00:13: Binance's official account repeats it and promises a full post-mortem.
- 00:14: ZachXBT reports that the Arbitrum Security Council froze ~$30.5M tied to exploiter address
0x3E2b…32d5. StalkChain data shows that address got 0.5 ETH from the main receiver at 21:29 UTC. - 00:43: The 14th altcoin (1.76M MORPHO) leaves the main wallet.
- 00:52: Binance raises the verified frozen total to about $3B. It says it is working with law enforcement, issuers and analytics firms to freeze more. ZachXBT puts it at over $2.83B at 01:01. We use Binance's figure.
01:00–02:00: swaps to ETH
- 01:01: Lookonchain reports the attacker finished selling seven altcoins, including 7.02M UNI and 217.5M ENA, for 70,480 ETH (~$158M).
- 01:03: StalkChain estimates Binance's SAFU fund at about 15,000 BTC (~$1.2B), less than the loss Binance has pledged to cover.
- 01:14: The main receiver sends 2,000 ETH to the parking wallet
0x8532…43d4, which now holds 197,460 ETH. - 01:16: 53.33M ZAMA comes back to the main receiver from the wallet it was sent to at 00:08.
- 01:17–01:18: Two more peels: 1.73M FET (in two transfers) and 45,218 PENDLE, to two new wallets.
02:00–03:00: Binance's first findings
- 02:25: Binance publishes its initial investigation. A compromised DevOps engineer's laptop let the attacker into a service container and submit unauthorized withdrawals. No evidence of a private key leak.
- 02:25: In the same post, Binance puts the total impact at about $6.3B and repeats that ~$3B is frozen on-chain. It will cover all losses from the SAFU fund and company funds, and publish an updated Proof of Reserves after remediation.
- 02:25: Deposits and withdrawals stay suspended. Binance has revoked the affected address authorisation and engaged law enforcement and blockchain intelligence partners.
What to watch next
- The ~470,900 ETH and ~17,270 BTC. Together that's ~$2.4B nobody can freeze, all sitting still. The first move toward a bridge, mixer or THORChain will show the laundering route. Bybit's stolen funds went through THORChain within days.
- The remaining unfrozen USDT on Tron and Ethereum, and whether Ripple freezes the ~$88.5M RLUSD.
- Binance's technical post-mortem. The first findings name a compromised DevOps laptop and a service container. We still need to know how that led to a signed EIP-7702 authorization for a hot wallet.
- The updated Proof of Reserves Binance promised after remediation.
- Withdrawals reopening, and whether Binance pays from its balance sheet. StalkChain estimates the SAFU fund at about 15,000 BTC (~$1.2B), well below this loss.
Deep dives
- How the Binance hacker used Aave to beat the USDT freeze
- EIP-7702 explained: how one signature drained Binance's hot wallet
- The Binance hacker rehearsed the attack four hours early
- Can USDT and USDC be frozen? What the Binance hack shows
- Was the Binance hack North Korea? The evidence and two false leads
- How to track the Binance hacker's wallets yourself
- The biggest crypto hacks ever, and where Binance ranks
Addresses to watch
| Chain | Address | Role |
|---|---|---|
| Ethereum | 0x5227f603c1ee34ce3c06efe6477003bdfccb2f8c | Main receiver (frozen stables + altcoins) |
| Ethereum | 0x8532fa14acaf483729c449b8458aeddb900543d4 | 197,460 ETH |
| Ethereum | 0xc887af690e0301cd4edbbce8f8d31b4ec65b286a | 137,602 ETH (USDT swaps + ENA sales) |
| Ethereum | 0x897c80d1a9729e94460e2bd93178bd5215158df3 | 78,415 ETH (Aave route) |
| Ethereum | 0x54401f80da97893a15d43566184635b6674bc942 | 32,954 ETH (altcoin sales) |
| Ethereum | 0x8d53903625b8e839b9df4bd28b0efb1cd6b8639a | Aave position: $60M USDT collateral, 19,762 ETH debt |
| Ethereum | 0x7f9dc988b46336ad536828fad50fa8fa1e5415e3 | 29,934 WBETH, untouched |
| Ethereum | 0xe7024ab80143b1ef843efe6a58368696cb87958d | 40.5M RLUSD |
| Ethereum | 0x7C8601d4645b93cea45F71e118A729332e6B5CA0 | Setup wallet (Tornado-funded) |
| Ethereum | 0x63e842B054Bd624a465454D533C33F573e9c6fAe | Drain contract |
| Ethereum | 0x3E2bf1ac6bf0934BBba6456C341c2EcbCED632d5 | Exploiter address (Arbitrum freeze) |
| Ethereum | 0x28c6c06298d514db089934071355e5743bf21d60 | Binance 14 (drained hot wallet) |
| Bitcoin | bc1q0mtc2f5agpkvlq6hhahmfr3hlr55kyfjhl2mnm | 18,270 BTC |
| Tron | TG5iBMQPrDzJJAUM8GMVBf1hRaJ1wvzsGi | 612.7M USDT (313M frozen) |
| Tron | TSpe5HC3PRD2svJcr1YoGszhHk2mtkyZ8A | 638.2M TRX |
You can paste any of the EVM addresses into the StalkChain wallet tracker to see live transfers.